When you visit a website over HTTPS, your browser needs a reliable way to determine whether the website’s security certificate can be trusted. This is where a root certificate becomes important. It acts as a trust anchor that helps browsers and operating systems verify the authenticity of SSL/TLS certificates.
SSL certificates are part of a larger trust system involving certificate authorities (CAs), intermediate certificates, and root certificates. Together, these components create a chain of trust that allows your browser to establish a secure connection with a website.
Understanding how this system works can help explain why browsers trust some certificates automatically while displaying security warnings for others.
What Is a Root Certificate?
A root certificate, also known as a root CA certificate, is a self-signed digital certificate issued by a trusted certificate authority. It sits at the top of the SSL/TLS certificate hierarchy and provides the foundation for verifying other certificates.
A certificate authority is an organization trusted to verify identities and issue digital certificates. Operating systems, browsers, and other software maintain lists of certificate authorities they trust.
When a browser encounters an SSL certificate, it does not simply trust the certificate because it exists. Instead, it checks whether the certificate can be traced back to a trusted authority.
This process is based on a certificate chain of trust.
How the SSL Certificate Chain Works
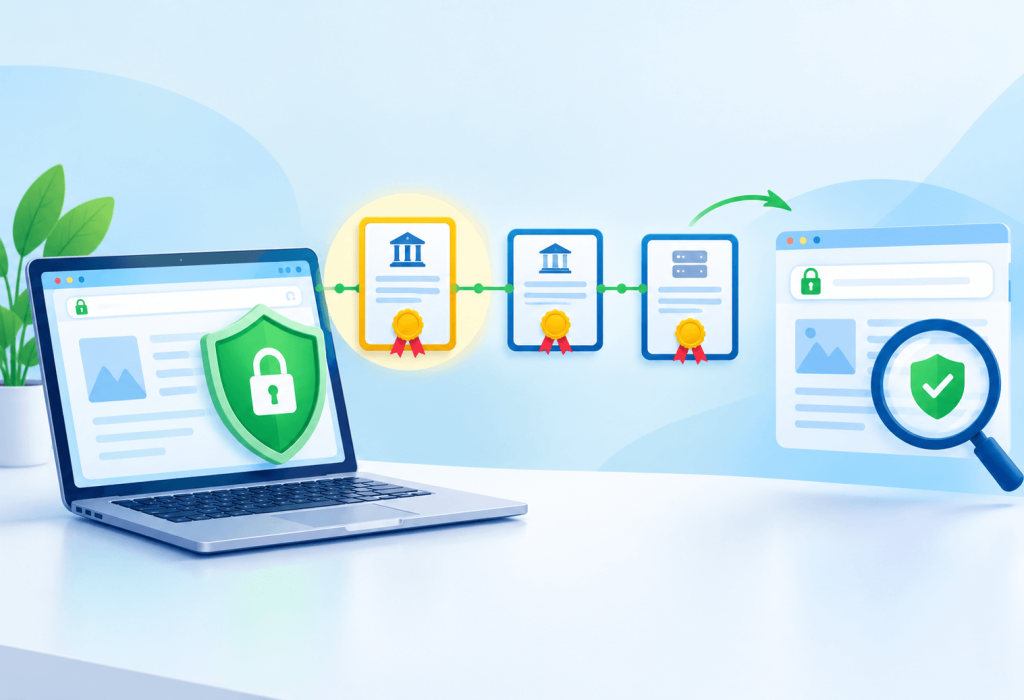
SSL/TLS certificates generally form a hierarchy rather than operating independently. A typical certificate chain contains three main levels:
- Root CA certificate – The trust anchor at the top of the hierarchy.
- Intermediate CA certificate – Issued by a root CA and used to sign website certificates.
- Server or end-entity certificate – Installed on a website and used to establish its identity.
When your browser connects to a secure website, it examines the website’s certificate and its issuer. If the issuer is not directly listed as a trusted authority, the browser can follow the chain to an intermediate certificate and eventually to a trusted root CA.
For example, the relationship may look like this:
Trusted Root CA → Intermediate CA → Website Certificate
If the chain can be validated successfully and other certificate requirements are satisfied, the browser can establish that the certificate comes from a trusted source.
The root certificate is especially important because it represents the final trust point in this hierarchy. Unlike certificates further down the chain, a root certificate is normally self-signed.
Why Are Root Certificates Self-Signed?
A self-signed certificate is one that is signed using its own private key rather than being signed by another certificate authority.
This might sound unusual because website certificates are normally validated through another trusted certificate. However, a root CA is at the top of the trust hierarchy, so there is no higher certificate authority that needs to sign it.
The trust comes from the fact that the root CA’s certificate has already been included in a trusted certificate store.
Browsers and operating systems maintain these stores and decide which certificate authorities are trusted. As a result, a root CA can serve as the starting point for validating certificates lower in the hierarchy.
What Does the Root Cert Mean?
If you’re wondering what does the root cert mean, it essentially means that the certificate belongs to the highest level of a trusted certificate hierarchy.
The word “root” refers to its position at the top of the certificate chain. It does not mean that the certificate is associated with a website’s domain name or that it directly secures every connection by itself.
Instead, it provides the foundation on which other certificates can be trusted.
For instance, when a website presents a certificate signed by an intermediate CA, your browser may check that intermediate certificate against a trusted root CA. If the chain is valid, the browser can recognize the website certificate as belonging to a trusted hierarchy.
This system allows certificate authorities to issue and manage large numbers of certificates without exposing their most important root keys every time a new website certificate is created.
Why Root Certificates Matter for Security
The security of the entire certificate ecosystem depends heavily on how trusted certificate authorities are managed.
If an attacker were able to compromise a root CA’s private key, they could potentially use it to create fraudulent certificates that appear trusted by browsers and operating systems.
For this reason, root CA private keys are protected extremely carefully. Certificate authorities commonly keep root keys offline and use them only when necessary.
Instead of using root certificates to sign website certificates directly, certificate authorities typically create intermediate CAs.
This creates an additional security layer.
For example:
Root CA → Intermediate CA → Website Certificate
If an intermediate CA is compromised, the potential impact can be limited to certificates associated with that intermediate authority. The root CA itself remains protected.
This separation helps reduce the risk associated with keeping a root CA operational for everyday certificate issuance.
How Root Certificates Are Distributed
Browsers and operating systems need access to trusted root certificates before they can validate SSL/TLS connections.
Rather than requiring users to install every trusted CA manually, operating systems and browser vendors maintain built-in certificate stores.
When you install an operating system, web browser, or other software that validates SSL certificates, it generally comes with a predefined collection of trusted root CAs.
These trusted lists can change over time.
Software vendors may add new trusted CAs, remove certificates, or modify trust settings as security requirements evolve. Updates are therefore an important part of maintaining a secure certificate ecosystem.
This is also why an older operating system or outdated browser can sometimes encounter certificate-related problems that newer software does not.
What Happens When a Certificate Isn’t Trusted?
If a website’s certificate cannot be connected to a trusted CA, your browser may display a security warning.
Several situations can cause this:
- The certificate is self-signed and isn’t trusted by the device.
- The certificate chain is incomplete.
- An intermediate certificate is missing.
- The certificate has expired.
- The certificate was issued for a different domain.
- The issuing CA is no longer trusted.
- The certificate has been revoked or otherwise fails validation.
A certificate warning does not necessarily mean that a website is malicious. It means the browser cannot establish the required level of trust.
However, users should take certificate warnings seriously, particularly when entering passwords, payment information, or other sensitive data.
Root Certificates vs. Intermediate Certificates
Root and intermediate certificates serve different purposes within the certificate hierarchy.
A root CA certificate sits at the top and acts as the trust anchor. It is generally self-signed and included in trusted certificate stores.
An intermediate CA certificate sits below the root. It is signed by a root CA or another trusted authority and is typically used to issue website certificates.
The separation provides an important security advantage.
Root certificates can remain highly protected while intermediate certificates handle regular certificate issuance. If an intermediate CA needs to be replaced or revoked, the root CA does not necessarily need to be replaced.
This hierarchical structure also makes certificate management more practical for certificate authorities.
How Browsers Verify Certificate Trust
When you visit an HTTPS website, the browser performs several checks before treating the connection as trusted.
It can examine:
- The website certificate.
- The certificate issuer.
- The certificate’s validity period.
- The domain name listed in the certificate.
- The certificate chain.
- The trusted CA store.
- Other applicable certificate policies and security requirements.
The browser then attempts to build a valid chain from the website certificate to a trusted root CA.
If the chain ends at a trusted authority and the certificates satisfy the required checks, the browser can establish the expected level of trust.
If the chain cannot be validated, the browser may show a warning instead.
Why Root CA Protection Is Important
Certificate authorities treat root CA private keys as highly sensitive security assets.
A compromised root private key could potentially undermine trust across a much larger portion of the certificate ecosystem. This is why root keys are typically subject to strict access controls, secure storage practices, and operational procedures.
Using intermediate CAs provides another layer of protection. The root CA can remain offline while intermediate authorities perform routine certificate issuance.
This design reflects an important security principle: the most powerful credentials should have the least exposure to everyday operations.
Finding Your Certificate Authority
If you want to determine which CA issued a website’s certificate, you can inspect the site’s SSL/TLS certificate using your browser or other certificate inspection tools.
The certificate details generally identify the issuer and provide information about the certificate chain.
Knowing the issuing CA can be useful when troubleshooting certificate problems, investigating trust issues, or understanding how a website’s HTTPS configuration is structured.
Related SSL/TLS Concepts
Understanding root certificates becomes easier when you also understand a few related concepts:
- Certificate Authority (CA): An organization responsible for issuing and managing digital certificates.
- Intermediate CA: A certificate authority operating below a root CA.
- SSL/TLS certificate: A digital certificate used to authenticate a website and support encrypted HTTPS connections.
- Certificate chain: The sequence connecting a website certificate to a trusted root CA.
- Trust store: A collection of certificates that an operating system or application considers trusted.
- HTTPS: The secure version of HTTP that uses TLS to protect communications.
These components work together rather than functioning as isolated technologies.
Conclusion
A root certificate is the foundation of the trust system used to validate SSL/TLS certificates. It sits at the top of the certificate hierarchy and allows browsers and operating systems to establish trust in certificates issued through intermediate authorities.
Root certificates are carefully protected because compromising one could have significant security consequences. By keeping root keys secure and using intermediate CAs for routine certificate issuance, certificate authorities can create a more controlled and resilient trust system.
For everyday users, the process happens mostly behind the scenes. Your browser relies on its built-in trusted CA information to determine whether a website’s certificate can be validated. Understanding this chain of trust makes it easier to understand HTTPS, browser security warnings, and the role certificate authorities play in keeping online connections trustworthy.
Read Also: