When a website uses HTTPS, SSL/TLS helps encrypt information exchanged between the user’s device and the web server while also verifying the server’s identity. When something goes wrong with this process, visitors may see warnings that prevent them from safely accessing the website. An ssl error can be caused by an invalid certificate, an outdated protocol, an incorrect domain name, or problems with the server configuration.
Although SSL is the older name, modern websites primarily use Transport Layer Security (TLS), the updated version of the protocol. SSL/TLS certificates help establish encrypted connections and allow browsers to verify that they are communicating with the intended server.
What Is an SSL Error?
An ssl error occurs when a browser or client cannot successfully validate an SSL/TLS certificate or complete the secure connection process. These problems can prevent users from accessing websites and applications securely.
A website’s SSL certificate is a data file installed on its server. It helps establish the server’s identity and enables the client and server to create encryption keys for a secure connection.
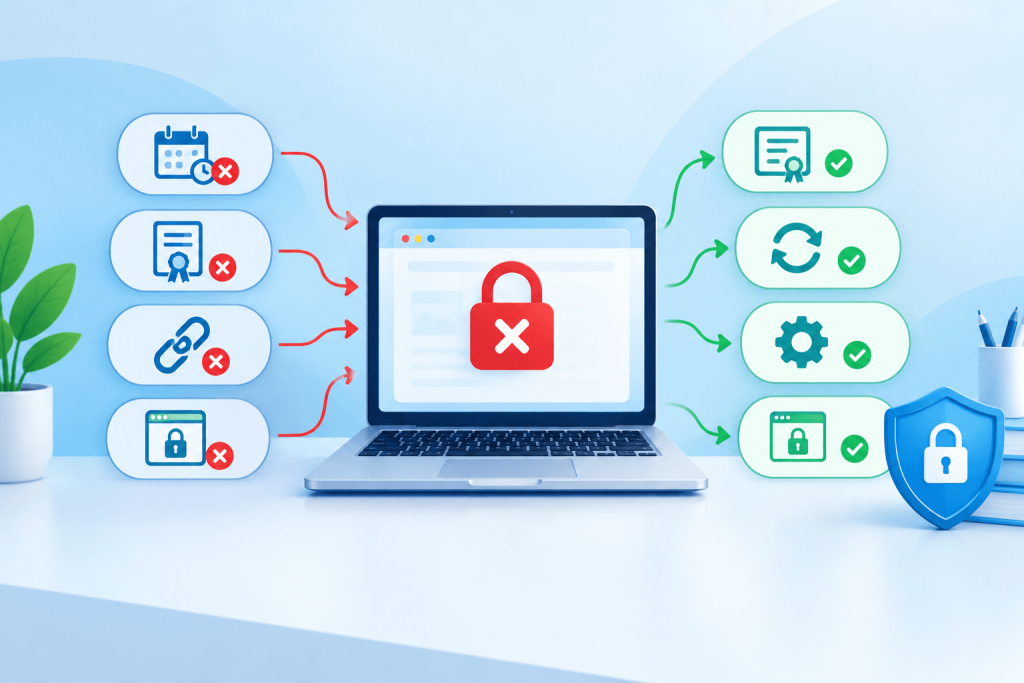
Common certificate and TLS problems include:
- An untrusted SSL certificate
- An outdated TLS version
- An expired certificate
- A certificate name mismatch
- Missing support for Server Name Indication (SNI)
Each problem has a different cause and may require a different solution.
SSL Certificate Is Not Trusted
Websites generally obtain certificates from a certificate authority (CA), an organization responsible for issuing and signing digital certificates. Browsers maintain lists of certificate authorities they recognize as trustworthy.
A self-signed certificate may not be trusted because it has not been independently verified by an external certificate authority. A certificate authority can also lose browser trust for other reasons.
When a browser cannot establish trust, visitors may see a warning such as “Your connection is not private.” This type of ssl certificate error can prevent visitors from loading the website normally.
How to Fix It
Website administrators should use an SSL certificate issued by a certificate authority supported by the browsers and systems used by their visitors.
If a certificate was issued by an authority that is no longer trusted, replacing it with a certificate from a currently supported CA can resolve the problem.
Wrong TLS Version
SSL and TLS protocols have evolved over time to address security vulnerabilities and improve authentication and performance. Modern web services increasingly require newer versions of TLS.
TLS 1.3 is the most current widely used version, while TLS 1.2 also remains in use. Websites configured to require modern protocols may reject connections from browsers, operating systems, or other clients that do not support the necessary TLS version.
For example, a client that cannot support the minimum TLS version required by a server may be unable to complete the TLS handshake.
How to Fix It
Users should keep their browsers and operating systems updated so they can support current TLS versions.
Website administrators should configure their servers to support appropriate modern TLS protocols rather than relying on outdated versions.
Expired SSL Certificates
SSL certificates are not valid indefinitely. They must be renewed periodically so the certificate information remains current.
When a certificate expires, a browser will no longer trust it. As a result, the TLS handshake cannot complete and the browser cannot establish the expected secure connection.
For website owners managing multiple domains and subdomains, keeping track of certificate expiration dates can become difficult.
How to Fix It
Administrators should verify that certificates covering their domains and subdomains are current and properly renewed.
An unexpected certificate warning can sometimes be caused by the user’s device rather than the website. If the device’s date and time are incorrect, the browser may incorrectly determine that a certificate has expired.
Checking and correcting the device clock can resolve the problem when an incorrect system time is responsible.
SSL Common Name Mismatch
A certificate name mismatch happens when the domain name in the SSL certificate does not match the URL the visitor is trying to access.
For example, the problem may occur when:
- A visitor enters a different domain or top-level domain.
- The URL includes “www” but that name is not covered by the certificate.
- The domain was typed incorrectly.
- The website operator configured the certificate incorrectly.
- Required domain names were left out of the certificate.
- The client or server does not properly support SNI.
A certificate must cover the legitimate versions of the domain that visitors are expected to use.
How to Fix a Name Mismatch
Website administrators should check that the domain names on the certificate are correct.
The Subject Alternative Name (SAN) field should include all legitimate domain variations that need to be protected. Correctly configuring these names can prevent browsers from receiving a certificate that does not match the requested website.
For users, checking that the website address was typed correctly is a simple first step.
Host Server Does Not Support SNI
Server Name Indication (SNI) is a TLS extension that allows multiple websites to operate on the same server while using different SSL certificates.
A server may host many domains under a single IP address. Without SNI, the server may not know which website the visitor is trying to reach and could provide the wrong certificate.
Think of a shared server as an apartment building. The IP address identifies the building, while SNI provides the equivalent of an apartment number. Without that information, the server may deliver the certificate belonging to another website.
When the wrong certificate is provided, the browser can report a certificate name mismatch.
How to Fix SNI Problems
Website operators should use hosting infrastructure that supports current TLS protocols and SNI.
Modern hosting environments generally support SNI, but older server configurations may require updating or reconfiguration. Encrypted SNI is also available as a related technology for improving privacy during connections.
SSL Certificate Error Meaning: What Should Website Owners Check?
The ssl error meaning depends on which part of the certificate or TLS connection has failed.
If visitors report certificate warnings, website administrators can start by checking:
- Certificate validity — Confirm that the certificate has not expired.
- Domain coverage — Make sure the certificate matches the domain visitors are accessing.
- Certificate authority — Check whether the issuing CA is trusted.
- TLS compatibility — Verify that the server supports appropriate TLS versions.
- SNI configuration — Make sure the server selects the correct certificate when multiple domains share an IP address.
- Client configuration — Consider whether outdated software or an incorrect device clock is contributing to the problem.
This process can help narrow down whether the issue originates from the website, server configuration, certificate, or visitor’s device.
How Cloudflare Helps Prevent Certificate Problems
Managing certificates manually can become challenging for organizations operating many websites, domains, and subdomains.
Cloudflare helps website operators avoid common certificate problems by automatically managing and renewing certificates for customer websites. Automation can reduce the administrative work involved in monitoring expiration dates and renewing certificates, particularly for organizations with large numbers of subdomains.
Automated certificate management does not eliminate every possible TLS configuration problem, but it can help reduce issues related to certificate expiration and manual renewal.
How Users Can Respond to an SSL Connection Error
When a browser displays a certificate warning, users should avoid entering sensitive information until they understand why the warning appeared.
A few basic checks can help:
- Confirm that the website address is spelled correctly.
- Check whether the device’s date and time are accurate.
- Update the browser and operating system.
- Try accessing the website again after updating the software.
- If the warning persists, contact the website administrator.
For website owners, reviewing the certificate’s expiration date, domain names, issuing authority, TLS configuration, and SNI support can help identify the source of the problem.
Conclusion
An ssl error can occur when a browser cannot validate a certificate or complete a secure TLS connection. Common causes include untrusted certificates, outdated TLS versions, expired certificates, domain-name mismatches, and servers that do not properly support SNI.
Understanding these issues makes troubleshooting easier. Website owners should keep certificates current, ensure certificates cover the correct domains, use trusted certificate authorities, support modern TLS versions, and maintain compatible server configurations. Users, meanwhile, should pay attention to browser security warnings and avoid submitting sensitive information when a certificate cannot be trusted.
With proper certificate management and up-to-date browser and server configurations, many common SSL/TLS connection problems can be prevented or resolved.
Read Also: